as we know cloud computing is basically renting someone's server or computer for personal or public use. so many of these cloud systems are left insecure due to developers making sensitive documents or folders publicly available or some of them have vulnerabilities that can be exploited. Today i shall explain how cloud hacking works , the risks and mitigation techniques to use.
What is an S3 Bucket??
In AWS, an S3 bucket is literally just a digital folder sitting on a server somewhere. Companies use them to store everything: website images, backup files, and sometimes (accidentally) highly sensitive customer data or passwords.
By default, AWS locks these folders down completely. But humans make mistakes. Developers often get frustrated when their code can't reach the folder, so they change the bucket's permission to "Public," meaning anyone on the internet can read it. Then, they forget to change it back.
How the attack works??
as an attacker, your favourite phrase is unauthenticated access lol. if a bucket is misconfigured as public, you don,t need to steal a password nor admin key. you can literally just ask the he AWS server, "Hey, what's in this folder?" and the server will just hand you the list. To do this, attackers use a specific flag in the AWS Command Line Interface (CLI): --no-sign-request. This flag tells AWS, "I am completely anonymous, I have no credentials, just let me in if the door is unlocked."
the attack commands look like this:
aws s3 ls s3:// <target S3-bucket-name> --no-sign-request
Ls = this stands for list, this is to list all the available files in the folder
Scenerio
To make this realistic i am going to do it a vulnerable S3 bucket
step 1: i have to make sure aws CLI is installed on my terminal
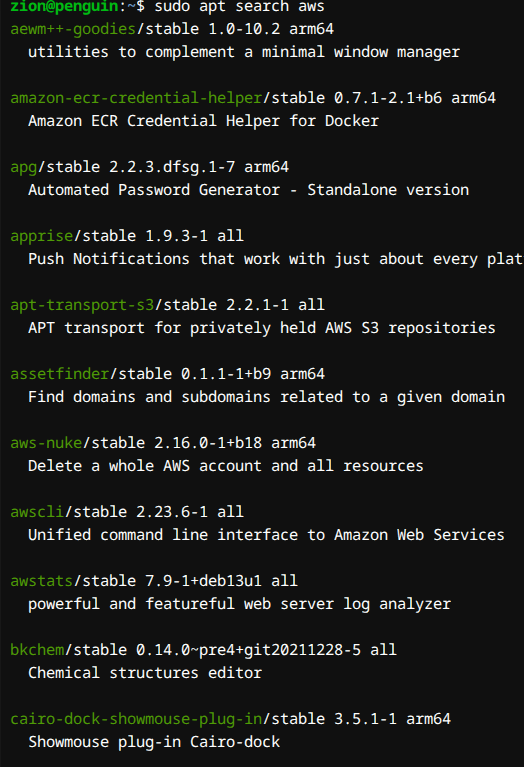
as you can see, i first searched through the Linux package manager to find aws CLI package. the package name is called awscli.
After installing the package, i then started the reconaisance on the S3 bucket.
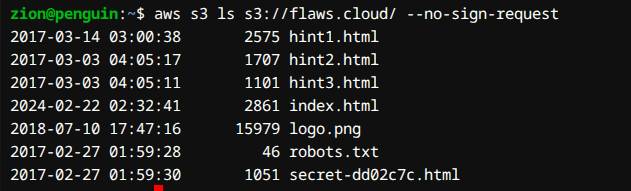
These are the files made publicly available, secret-dd02s7c.html looks suspicious. I will check it out.
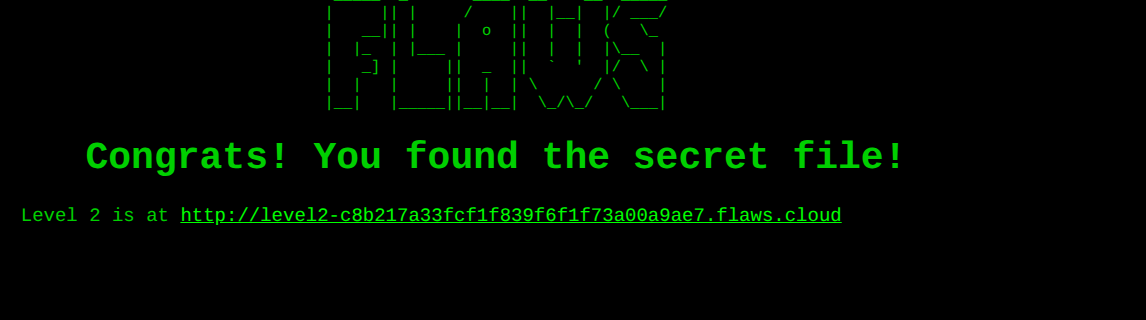
in a real situation maybe a company that might be a private document maybe source code, financial information or the .env file of the company database. this is only one of the mistake that can lead to cloud being compromised.
About the author
- just a simple guy
Comments
Join the discussionNo comments yet. Be the first to comment.